Key Points to Keep in Mind When Choosing an Electronic Archiving Provider Verify the provider’s compliance guarantees: archiving standards, certifications, and any eIDAS qualification status must meet your organization’s requirements. Examine the...

Articles
Discover the power of qualified timestamping in proving the exact time and integrity of your digital evidence. Our blog posts explain how timestamping enhances trust, supports legal admissibility, and seamlessly integrates into your digital workflows for secure, automated proof management.
Key Points to Keep in Mind When Choosing an Electronic Archiving Provider Verify the provider’s compliance guarantees: archiving standards, certifications, and any eIDAS qualification status must meet your organization’s requirements. Examine the...
Key Points to Consider When Choosing an Electronic Seal Provider Choose the right level of electronic seal—simple, advanced, or qualified—based on your organization’s legal requirements and security needs. Verify the provider’s security measures:...
Key Takeaways on Post-Quantum Cryptography Post-quantum cryptography refers to algorithms designed to withstand attacks from both quantum and classical computers. Future quantum computers could compromise electronic signature and certification...
Key points to remember about proof of musical creation Keeping successive versions of a song allows you to trace its creation. The creative journal documents the designer's choices and any contributions made by AI. Qualified time stamping...
According to an article by Jean Albert, president of the Agency for the Protection of Programs (APP). Key takeaways on music and AI Music production using AI raises issues related to visibility and compensation. Music streaming platforms and music...
Key points to keep in mind when choosing a qualified timestamping provider eIDAS Qualification: Verify that the timestamping service is included on an official European trusted list and that its qualification is active. Technical guarantees:...
Key Takeaways on LegalTech Issues Digitisation does not eliminate the challenges associated with evidence: Legaltech companies must be able to guarantee the origin, integrity, and traceability of digital documents. Gaps in documentation trails...
I. Evidence at the heart of the assessment of originality (European and comparative case law) But this is where our era changes everything. We no longer live in a “slow” world, where creation followed rare, tangible steps that were easily visible...

Key takeaways on the evidential value of time tracking The legal requirement to record working hours does not guarantee that the data produced will be admissible as evidence in court. The CJEU requires a system that is “objective, reliable, and...
Key points to remember about proof of transaction in Fintech Clicking "Invest" constitutes a financial order as defined by the ECSP regulations: its exact date may determine the order's validity. An uncertified internal log does not constitute...
Key points to remember about qualified electronic signatures The eIDAS Regulation distinguishes between three levels of electronic signature: simple, advanced and qualified. Only a qualified electronic signature benefits from a presumption of...
Key points on in-house software development Vibe coding makes software development accessible to all profiles, including non-technical users. Developing software internally (through a dedicated IT team or vibe coding) transfers responsibilities...
Key facts about AI development Without process traceability, copyright protection of AI-generated code becomes difficult to defend Keeping and time-stamping the dialogue with the model (prompts, responses, iterations) enables you to pre-constitute...
Key points to remember about document fraud risk The risks of document fraud can be many: financial, reputational, legal... Risk control is based on three guarantees: integrity, date certainty and origin. Prevention becomes truly effective when...
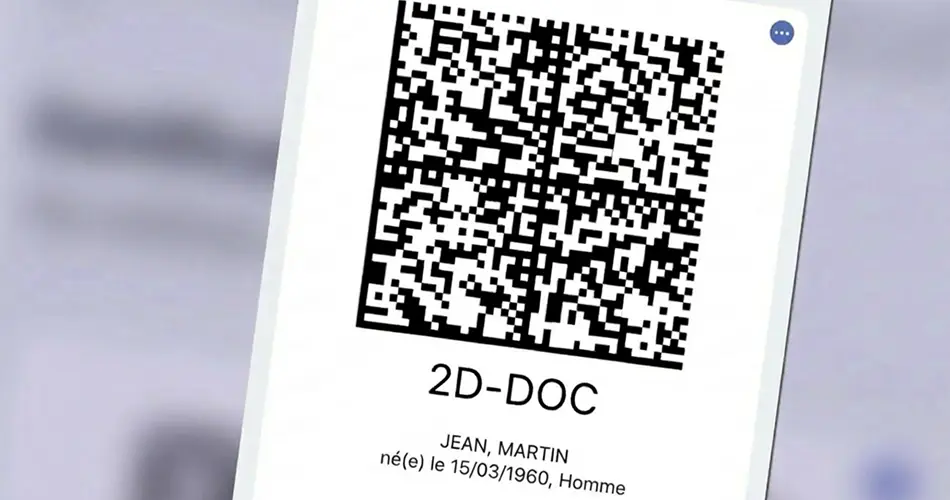
Key takeaways 2D Doc secures data encoded within a 2D barcode, readable using a dedicated scanner. It is particularly useful for supporting documents frequently exposed to falsification (e.g. identity cards, tax documents, invoices). Electronic...
Key takeaways Digitising HR documents is not sufficient to guarantee their legal validity. Evidential weight depends on three conditions: an appropriate electronic signature, qualified timestamping and evidential electronic archiving. Certain HR...
Key points on the DMCC Act Drip pricing prohibited: the total price must be displayed from the first price indication, including all mandatory charges. Fake reviews prohibited: it is forbidden to publish, commission or facilitate them. Platforms...
Key points to remember about cryptography applied to evidence Key points to remember about cryptography applied to evidence A hash function transforms data into a fixed-size hash value; it is designed to operate in one direction. The hash serves as...
Key takeaways to note about timestamping The TSA (Time-Stamping Authority) is the provider that issues timestamp tokens in accordance with a standard protocol (most commonly RFC 3161). The TSP protocol defines a request (fingerprint, algorithm,...
Key takeaways on PKI and certificates The PKI organises the issuance, management and validation of certificates used for signing or sealing. The certification authority (CA)...
What is the RFC 3161 protocol? RFC 3161, sometimes referred to as the Time-Stamp Protocol (TSP), is an open standard that enables a timestamping authority (TSA) to produce a timestamp token linking a cryptographic fingerprint (hash) of data to a...
What is an API? An API (Application Programming Interface) is a programming interface that allows one software application to call functions exposed by another software application according to published rules (methods, parameters, formats and...
What is integrity? The integrity of data or a document refers to the absence of alteration: the content presented must be identical to the content that was originally created or stored. In the context of electronic records, integrity is an explicit...
Key takeaways to remember about the burden of proof Electronic evidence has the same legal value as a paper document (Articles 1365 and 1366 of the French Civil Code). The burden of proof rests with the claimant (the party asserting the facts), but...
Key takeaways on the European Digital Identity The European Digital Identity, through the EUDI Wallet, seeks to establish an interoperable means of identification recognised across the European Union. It enables users to prove certified attributes...
Key takeaways A digital document has no inherent legal value: its admissibility depends on its ability to establish authenticity, integrity and a reliably established date. A simple file (PDF, Word) can be altered without any visible trace, which...
Key points to note regarding the protection of medical data: Medical data constitutes special category data within the meaning of the GDPR: its processing requires enhanced safeguards and the ability to demonstrate compliance. Protection rests on...
Key takeaways eIDAS compliance governs digital trust services in Europe and determines the legal effect of electronic signatures, seals and timestamps. Qualified services benefit from a presumption of reliability recognised throughout the European...
Key points on Reg Tech Reg tech encompasses technological solutions dedicated to managing and overseeing regulatory compliance. It addresses a dual challenge: operational efficiency and the ability to produce verifiable evidence. Compliance can no...
Key points on dematerialised contracts A dematerialised contract has the same legal value as a paper contract, provided that the identification of the signatory and the integrity of the document are guaranteed (Articles 1366 and 1367 of the Civil...
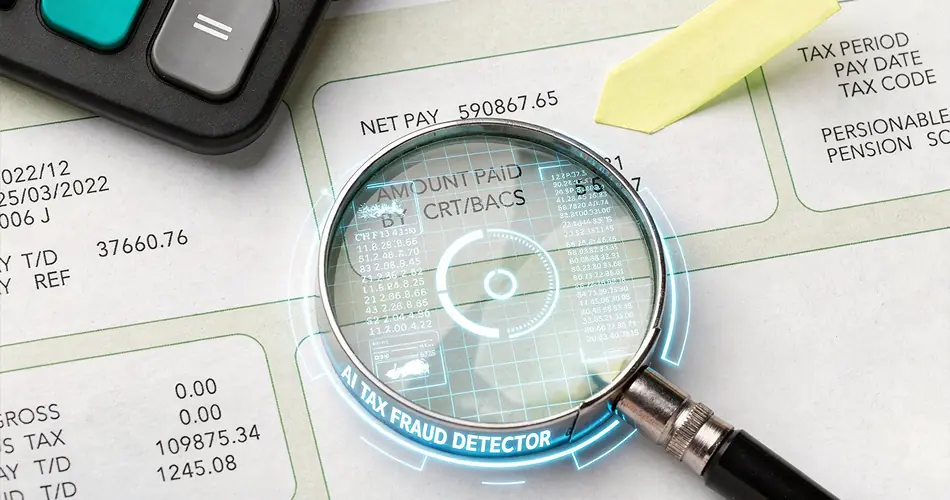
Key takeaways AI is becoming a major tool to fight social and tax fraud, but it is still underused by public authorities. AI technologies (machine learning, deep learning, generative AI) can process large volumes of data and detect increasingly...
Key takeaways on CLM Contract lifecycle management (CLM) enables the structured organisation and effective oversight of the contract lifecycle, from drafting through to archiving. CLM tools enhance contractual governance by centralising documents,...
Key takeaways about traceability in digital registered mail Registered mail serves an evidential function: it is used to prove that a legally significant communication was sent and received. The evidential value of registered...
Key points to keep in mind about the authenticity of a document Authenticating a document means verifying its origin, its integrity and its conformity with the original. Documentary fraud is increasing: 69% of French companies are targeted by...
Key takeaways of this interview: Trust in AI is not limited to the quality and lawfulness of training data. Above all, it requires effective capabilities for evaluating, testing and monitoring systems and their uses. The availability and quality of...
Key points on trust service providers A trust service provider (TSP) delivers trust services intended to guarantee the authenticity, integrity and legally reliable dating of electronic documents and data. The reference legal framework is the eIDAS...
Key takeaways from this interview Copyright protection for a work created using AI requires proof of substantial human intervention, as content generated solely by an AI system is not eligible for protection. Traceability of the creative process...
Key takeaways on Legal Tech and AI 71% of legal departments already use generative AI for their research AI can analyse and sort evidence, but does not certify either its date or its integrity Deepfakes represent a growing threat to the...
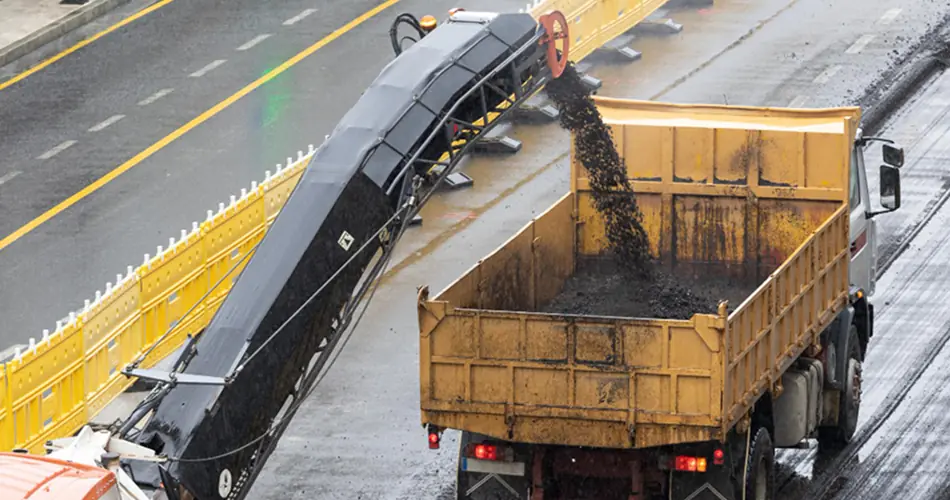
Key points to remember about the French Weighing quality standard: The Weighing quality standard (NF P 98-750) scheme addresses an evidential requirement: securing the traceability of asphalt deliveries and limiting fraud (theft, falsification,...
Key points to remember about HSMs: An HSM is a hardware device dedicated to the secure protection, generation and management of cryptographic keys. It provides the technical foundation for digital trust...
Key points to remember on document fraud detection Document fraud is based on a deliberate intention to deceive and can involve any type of document (contracts, invoices, documentary evidence, identity documents). There are many forms of fraud:...
Key points on admissible digital evidence An electronic record has the same evidential weight as a paper document, subject to certain conditions. Two fundamental requirements apply: identification of the author and integrity of the document. The...
Key points on NTP Protocol The NTP protocol is a technical mechanism designed to synchronise the clocks of computer systems within a network. This shared time reference becomes decisive where the date and time of an event are relied upon for...
Key points about hashing Hashing generates a unique, irreversible fingerprint that enables the integrity of a document to be verified without disclosing its content. Any alteration to the file immediately changes the fingerprint, making attempts at...
Key takeaways DORA regulation establishes a unified EU framework for managing digital risks, ensuring that all financial institutions and their technology providers can maintain operations even during severe IT disruptions. The regulation...
Key takeaways Corporate digital identity is a pillar of digital trust. It enables authentication of the issuing legal entity and ensures the integrity of the documents it produces. Failure to address this identity exposes organisations to...
Key takeaways on the NIS 2 Directive The NIS 2 Directive strengthens the European cybersecurity framework and applies to a broader range of public and private sector organisations. It distinguishes between two categories of entities, essential...
Key takeaways: deepfakes and digital evidence The deepfake threat is real: $25.5 million lost through a fake videoconference; 70% of French companies targeted by fraud in 2022. The European legal framework is strengthening: eIDAS 2 and the AI Act...
Key takeaways Digital trust has become a strategic issue in securing digital workflows in the face of the increase in cyberattacks, fraud and regulatory requirements. It is based on four core pillars: data integrity, authenticity of the issuer,...
Key takeaways Digital consent does not always take the form of a signature. A click, a ticked box or the validation of a form must nevertheless be demonstrated in a reliable and legally enforceable manner. Qualified timestamping provides a legally...
Key takeaways The evidential value of an electronic signature is based on the identity of the signatory, the integrity of the document and the reliability of the signing process, beyond the mere eIDAS signature level. Even a qualified electronic...
Key takeaways on high-risk AI operators The AI Act establishes a risk-based approach, with enhanced obligations for so-called “high-risk” AI systems used in sensitive sectors. The organisations concerned are not limited to developers, but also...
Key takeaways Claims management is becoming increasingly digital, with widespread use of online claims notifications and strong expectations of simplicity and speed on the part of policyholders. This transformation requires insurers to reassess...
Key takeaways The dematerialisation of exchanges is profoundly reshaping the law of evidence and requires legal professionals to adapt their strategies in the face of increased risks of falsification and challenge. Digital evidence is legally...
Key takeaways Market data represents a high strategic cost for financial institutions, with significant risks of overspend arising from audits and a lack of transparency regarding actual usage. Discrepancies between the effective use of financial...
Key takeaways The selection of a Qualified Trust Service Provider is a strategic decision to ensure the legal effect, integrity and regulatory compliance of digital documents and transactions. An eIDAS-compliant solution must deliver high...
Key takeaways Digital transformation has placed Chief Legal Officers (CLOs) at the centre of dematerialisation challenges, with responsibility for reconciling operational efficiency, legal certainty and regulatory compliance. Legal departments must...
Key takeaways on eIDAS 2.0 Since 20 May 2024, the eIDAS 2.0 Regulation strengthens the European legal framework for electronic transactions by extending its scope and increasing the level of security applicable to trust services. Each Member State...
Key takeaways on Omnibus Directive and promotional prices The Omnibus Directive, which entered into force on 28 May 2022, significantly strengthens consumer protection against misleading commercial practices, particularly within the digital...
Key takeaways on qualified electronic timestamping Electronic timestamping consists of linking digital data to a specific date and time in order to prove that the data (and its content) existed at that precise moment, generally through a trusted...
Key takeaways Timestamping provides an immutable and verifiable record of when an electronic invoice is created, sent, or received, ensuring integrity and traceability. By leveraging cryptographic mechanisms, timestamping protects electronic...
Key takeaways on eIDAS qualified timestamping Electronic timestamping makes it possible to prove that a digital document existed at a specific date and time and that it has not been altered since. When it is eIDAS-qualified and issued by a...
Key takeaways In matters of intellectual property, electronic timestamping makes it possible to establish evidence of prior creation and integrity of digital works. From a regulatory perspective, it facilitates the demonstration of compliance, in...
Key takeaways on timestamp tokens A timestamp token reliably associates a date and time with a data item in order to prove its existence and integrity at a given point in time. Evidency’s timestamping solution is based on recognised cryptographic...